Drawing the Credential Map: Why Your Team Can't Name Every Key It Owns
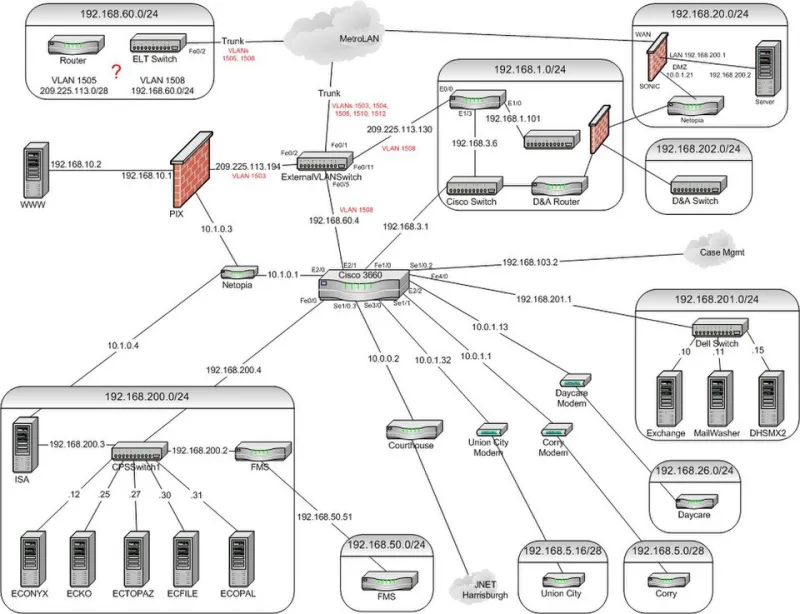
Photo: No machine-readable author provided. Dantic assumed (based on copyright claims)., CC BY-SA 3.0, via Wikimedia Commons
Ask any senior engineer to whiteboard their system architecture and they'll do it without hesitation. Ask the same team to list every API key, service token, and access credential their product uses — including the ones issued three years ago to a vendor nobody talks to anymore — and the room goes quiet.
That silence is the vulnerability. Credentials that no one can name are, by definition, credentials no one rotates, scopes, or revokes. And unlike a misconfigured firewall, they don't announce themselves. They sit quietly in a .env file, a CI variable, a Lambda environment block, waiting for a leaked repository or a departed contractor's laptop to make them someone else's problem.
Treat Credentials Like Geographic Data
At Map2Key, we spend a lot of time thinking about how people represent physical spaces. A good map does three things: it shows what exists, it shows where it is, and it gets updated when reality changes. A credential inventory should work the same way — and most don't, because most are built as audit artifacts rather than as maps.
The distinction matters. An audit is a snapshot with a deadline. A map is a system of record with an update loop. When your security team treats the inventory as a compliance checkbox, it decays within a quarter. When they treat it as infrastructure, it becomes the reference layer every other decision — rotation schedules, blast-radius analysis, vendor offboarding — is drawn against.
The Discovery Pass: Finding What You Forgot
Before you can map credentials, you have to find them. Start with a brute-force sweep across every place keys tend to hide:
- Source control history, not just the current tree. Tools like TruffleHog and Gitleaks scan commit history for high-entropy strings and known key formats, because a secret removed in a later commit is still exposed in the log.
- CI/CD configuration. GitHub Actions secrets, GitLab CI variables, and Jenkins credential stores accumulate tokens that outlive the pipelines that used them.
- Cloud provider metadata. AWS IAM's credential report, GCP service account listings, and Azure Entra app registrations reveal machine identities nobody has reviewed since onboarding.
- Developer workstations. Local
.envfiles and shell histories are where keys go to escape the inventory entirely. - Third-party dashboards. Your mapping provider, payment processor, SMS gateway — each one issued you a key. The vendor side of the ledger is as important as yours.
Expect the first pass to be humbling. Teams running this exercise for the first time routinely discover two to three times more credentials than they documented, including production keys embedded in test fixtures and tokens for services that were decommissioned but never deprovisioned.
Building the Map Itself
Raw discovery output isn't useful to anyone but the person who ran the scan. The next step is structuring it. For each credential, record five attributes:
- Owner — the team, not the individual, accountable for rotation and revocation.
- Scope — what the key can actually do, per the provider's permission model, not what it was intended to do.
- Location — every system where the value appears, including backups and build artifacts.
- Lifetime — issued date, last-rotated date, and whether expiration is enforced.
- Dependency — which product features break if the key is revoked tomorrow.
That last attribute is the one teams skip, and it's the one that turns an inventory into a map. Knowing that a Stripe key lives in three services is data. Knowing that revoking it takes down checkout, subscription webhooks, and refund processing is operational intelligence. It's the difference between a table and a topology.
Visualize it however your team already works — a graph in your internal wiki, a dedicated secrets-management platform, even a spreadsheet with disciplined ownership. The format matters less than the maintenance loop: every new credential gets added at creation time, every offboarding triggers a review, every quarter includes a diff against the discovery scan.
Making the Map Stick
The failure mode of every credential audit is the follow-up that never happens. Three practices prevent it:
Wire discovery into CI. Run Gitleaks or a similar scanner on every pull request so new secrets surface before merge, not after. Discovery becomes continuous instead of annual.
Tie the map to offboarding. When an engineer or vendor departs, the credential map — not tribal knowledge — determines what gets rotated. HR-driven checklists miss keys; a map query doesn't.
Rank by blast radius, not by age. A stale read-only key for a test environment is noise. A broadly-scoped production token with no rotation history is the headline waiting to happen. Triage accordingly, and fix the high-radius items first even if the long tail stays messy.
The Payoff
A maintained credential map changes the character of security incidents. When a provider announces a breach or a key appears in a public repository, the response shifts from days of archaeology to a targeted revocation with a known dependency list. The map doesn't prevent every leak — nothing does — but it collapses the time between detection and containment, which is where real damage lives or dies.
Your architecture diagram shows how the system works. Your credential map shows how it can fail. In 2024, with secret sprawl implicated in a steady drumbeat of US breach disclosures, the second document deserves the same care your team already gives the first.