The Exit Interview Nobody Scheduled: Offboarding an Enterprise Customer Without Leaving Credentials Behind
Photo: Loominade, CC0, via Wikimedia Commons
When an enterprise customer decides not to renew, most engineering teams treat it as a billing event. The contract lapses, the account flag flips to churned, and the account executive sends a courteous farewell email. Meanwhile, the customer's API keys keep authenticating. Their geofences keep evaluating. Their provisioned credentials — the ones embedded in their fleet trackers, kiosks, and mobile apps — continue to resolve against your mapping infrastructure exactly as they did the day before the termination email went out.
This is the handoff problem, and it is one of the most under-engineered workflows in SaaS platforms that deal with location and access. Onboarding gets roadmaps, design reviews, and dedicated integration engineers. Offboarding gets a Slack message and a shrug.
The Blast Radius You Discover Too Late
The first time most teams attempt a serious customer offboarding, they learn their real dependency graph the hard way. A logistics company in the Midwest churns from a delivery-orchestration platform, and three weeks later support tickets surface because their old integration is still pinging tile endpoints. Worse, some of those calls are succeeding — because a service key issued during a 2021 pilot was never scoped to the contract term.
Blast radius in these situations tends to cluster in three places:
Embedded credentials. Keys baked into firmware, mobile binaries, or third-party hardware cannot simply be revoked on a dashboard. They live in trucks, warehouses, and devices in the field, and they will keep presenting themselves at your edge until someone makes them stop working.
Derived data. Geofences, custom map layers, cached route preferences, and address datasets the customer uploaded. Deleting them is straightforward; knowing where every copy lives — replicas, caches, analytics pipelines, backups — is not.
Shared infrastructure. Webhooks pointed at customer endpoints, OAuth grants issued to the customer's downstream tools, and service accounts created for the implementation. Each of these is a lingering trust relationship that outlives the contract.
The uncomfortable truth is that most teams cannot enumerate this inventory on demand. They discover it by tracing production traffic after the fact, which is the most expensive possible way to learn it.
Treat Offboarding Like an Incident, Not an Invoice
The teams that handle this well borrow a page from incident response. A customer termination gets a declared owner, a timeline, and a runbook — before it ever happens.
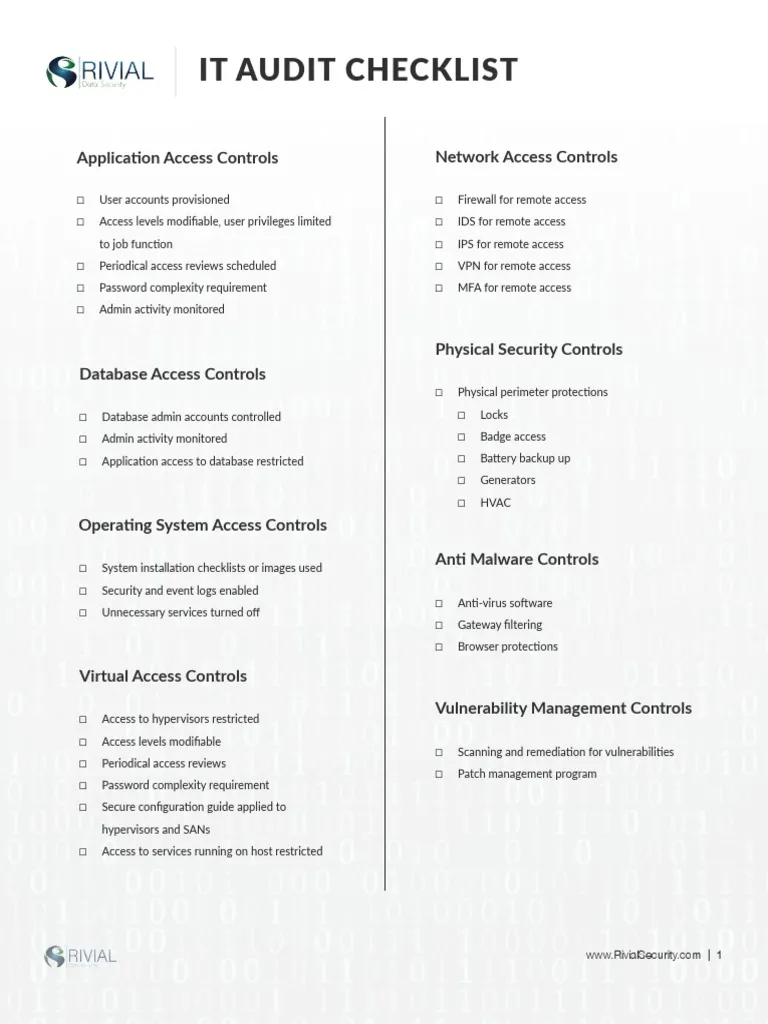
Start with a credential inventory generated at onboarding, not at exit. Every key, token, and certificate issued to a customer should carry metadata: contract ID, issue date, rotation history, and whether it is user-facing or service-to-service. When the churn notice arrives, that inventory becomes your work queue instead of an archaeology project.
Next, sequence the revocation. A hard cutover on the contract end date sounds clean, but it breaks customers mid-transition and generates hostile support tickets. Better practice is a staged degradation: read-only access after the end date, then a 30-day sunset window with prominent deprecation headers on every API response, then full revocation. Each stage should be automated off the contract record, not triggered by a human remembering to click.
Finally, design for the callback. Churned customers return — sometimes two years later, sometimes through an acquisition. Offboarding should archive configurations and permission structures in a restorable state, so a returning customer can be re-provisioned in hours rather than rebuilt from email threads.
The Location-Specific Wrinkle
Platforms with geospatial components carry an extra obligation: location data often encodes the customer's own operational footprint. A churned retailer's geofences describe their store network. A departed delivery company's route history reveals logistics patterns. Retaining this data longer than contractually justified is not just a storage cost — it is a compliance liability under state privacy statutes like the California Consumer Privacy Act and a contractual exposure if your agreement included data-deletion commitments.
Your offboarding pipeline should therefore distinguish between three data classes: credentials (revoke fast), derived configurations (archive briefly, then delete), and raw location history (delete on schedule, with cryptographic attestation if the contract demands it).
Make the Runbook a Product Feature
Here is the strategic point: offboarding is not just hygiene. Enterprise buyers increasingly audit how vendors handle exit. A platform that can demonstrate a documented, tested, automated offboarding workflow — with evidence of revocation and deletion — closes deals that a platform with a shrug cannot.
If your access-management layer cannot answer the question "show me exactly what happens when this customer leaves," that gap is not an operational nuisance. It is a sales objection waiting to happen. Build the pipeline now, while the departure is hypothetical, because the first time you run it should never be under the pressure of a real termination notice.