Room Keys and Rate Limits: What a Hotel Lobby Can Teach Your Onboarding Flow
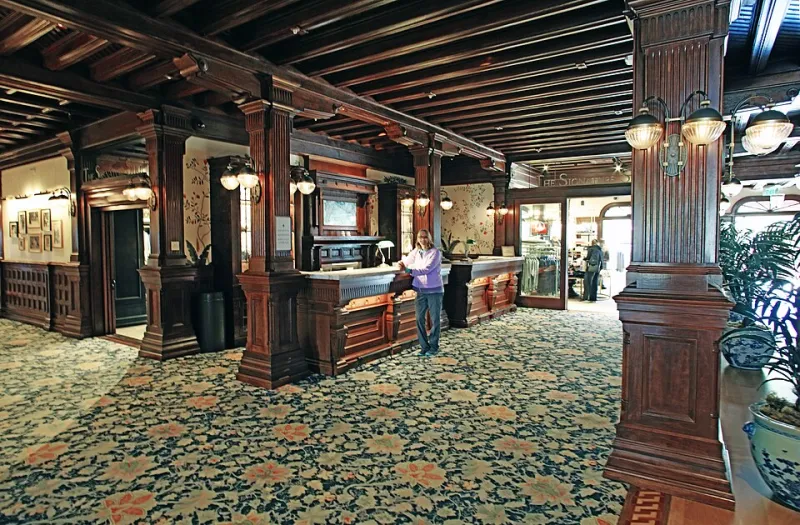
Photo: KMPhotoLA1, CC BY-SA 4.0, via Wikimedia Commons
The Best Onboarding Flow in America Isn't on a Screen
Consider the humble hotel check-in. A traveler arrives with no prior relationship beyond a reservation, presents one form of identification, and walks away minutes later holding a credential that opens exactly one room, on exactly one floor, until exactly one morning. Floor access is scoped. Expiration is automatic. The front desk can reissue a lost key in seconds without revoking anyone else's.
Now consider the typical developer onboarding flow for a mapping or access-management API. Sign up, verify email, wait for account approval, hunt through documentation to figure out which endpoints a sandbox key actually unlocks, file a ticket when the key silently lacks the scopes the tutorial assumed, and — if the developer ever leaves — hope someone remembers to clean up the credentials they created along the way.
The hotel wins, and it wins consistently, across thousands of properties run by teams with no shared engineering culture. That consistency is the lesson. Check-in is a well-designed API: it has a clear contract, observable state, and a graceful end-of-life path. Most developer onboarding flows have none of the three.
Time-to-First-Key Is the Only Metric That Matters
Hotel operators understand something platform teams often miss: the moment of issuance is the moment of commitment. A guest standing at the desk is a conversion. A guest standing in line is a churn risk. Every step between arrival and a working key is friction, and good properties have spent decades shaving it down — kiosks, mobile keys, pre-arrival verification.
Developer platforms should measure the same thing. Not signups, not dashboard logins — time from account creation to the first successful authenticated API call. If that number is measured in days rather than minutes, the flow is the problem. Every hour a developer spends waiting for manual approval or reverse-engineering scope documentation is an hour a competitor with a self-serve sandbox is using to close the deal.
The hotel analogy also clarifies why fast issuance is safe. Hotels issue keys instantly because the credential is narrowly scoped by design. A room key cannot open the cash office. Platforms that delay key issuance pending manual review are usually compensating for scopes that are too broad — the credential is dangerous, so the process must be slow. Fix the scoping and you can fix the latency.
Scopes Should Read Like Room Privileges
Ask a hotel guest what their key does and they'll tell you without hesitation: room 1412, through Thursday, fitness center included. Ask a developer what read:assets write:config means in the context of your geofencing service and you'll likely get a shrug.
Scope design suffers from a vocabulary problem. Names are either too technical to be meaningful or too coarse to be safe. The hotel model suggests three properties every scope set should have:
- Spatial legibility. A room number tells you where the credential works. Scopes for location-based services should map intuitively to resources — which maps, which fleets, which buildings.
- Temporal legibility. Checkout is printed on the key envelope. Credential expiry should be equally explicit, not an undocumented default buried in account settings.
- Failure legibility. When a guest taps a key against the wrong door, the lock simply doesn't open — and the front desk can explain why in one sentence. A 403 from an API should be just as diagnosable.
Three Onboarding Flows, Three Failures
We've all signed up for dozens of developer platforms. Without naming vendors, three failure patterns recur so often they deserve a teardown.
The velvet rope. Signup completes instantly, but the API key arrives 'within 1–2 business days' after a sales review. This is the members-only lounge model of check-in: it signals that the platform is for someone else. It's defensible for enterprise-only products and indefensible for anything with a self-serve tier.
The master key. One credential, every permission, issued at signup because granular scoping 'is on the roadmap.' The hotel equivalent is handing every guest a key to the whole building. It works until it doesn't, and then it works catastrophically.
The no-checkout hotel. Keys never expire, departed guests retain access, and there is no desk clerk to return to. Credentials accumulate across former contractors, abandoned proof-of-concepts, and departed employees. Every access audit eventually discovers this hotel has been running for years with an unknown number of outstanding keys.
Design the Checkout Before the Check-In
The deepest lesson from hospitality isn't about issuance at all — it's that the flow was designed with an ending in mind. Checkout is a scheduled, expected, low-drama event. Housekeeping can't enter the room afterward, and the front desk system reflects the change immediately.
Access platforms should treat offboarding with the same intentionality. Expiry should be a first-class property of every credential, not a cleanup script. Departure workflows — whether an employee leaving the company or a customer churning off the platform — should trigger revocation as a designed step, not an afterthought discovered during the next audit.
A developer who checks into your platform should have an experience as unremarkable and reliable as a good hotel stay: fast issuance, obvious privileges, and a clean exit. Anything less, and you're asking your users to sleep with the door unlocked.